 017 1223 6015
 017 1223
Showing all 9 resultsSorted by latest
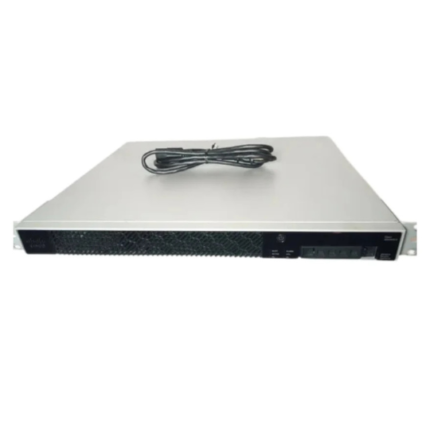
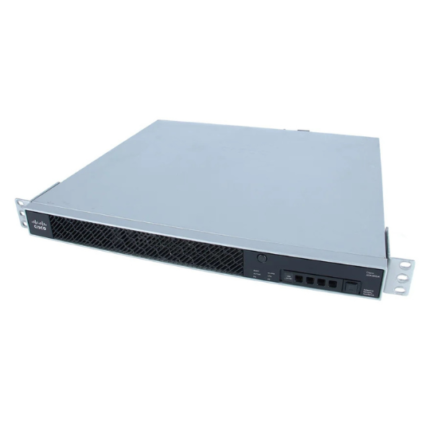
Cisco ASA 5515-X Firewall
Original price was: 56,000৳ .40,000৳ Current price is: 40,000৳ .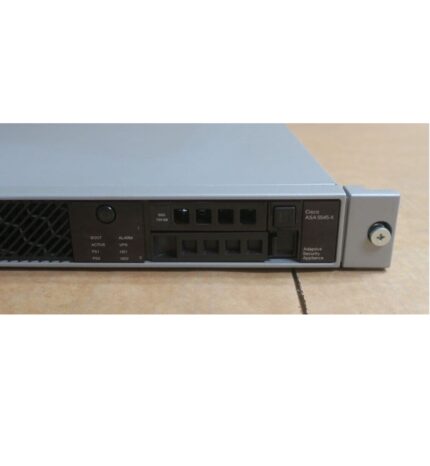

Cisco ASA 5545-X
35,000৳

Cisco ASA 5520 Series
18,500৳

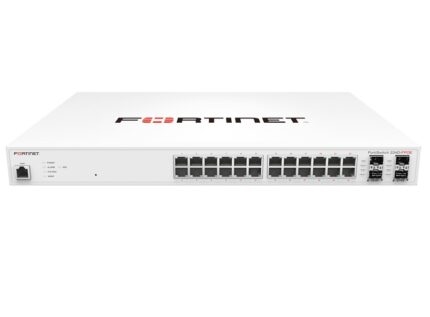
Fortinet FortiSwitch 224D-FPOE
55,000৳


Cisco Firewall ASA5585-S10-K9
85,000৳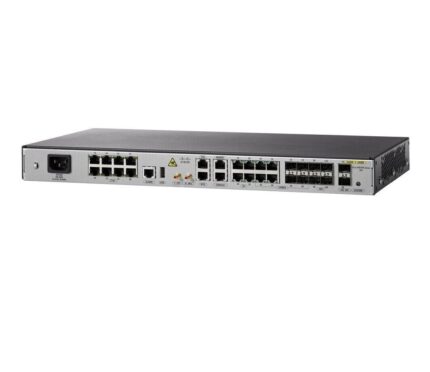
Cisco ASR 901 Series 10G
65,000৳Firewalls — Enterprise Network Security Solutions for Bangladesh
Welcome to our comprehensive firewall selection. Whether you are protecting a small business network, securing an ISP backbone, or implementing enterprise-grade security — we have the right firewall solution for your needs.
What Is a Firewall and Why Does Your Network Need One?
A firewall is the critical security guardian between your internal network and the internet. Its job: inspect all traffic entering and leaving your network, block threats, and enforce security policies.
Without proper firewall protection:
- ❌ Hackers can directly access your servers
- ❌ Malware spreads freely through your network
- ❌ Sensitive business data is exposed
- ❌ No visibility into network threats
- ❌ No protection from DDoS attacks
With enterprise firewall protection:
- ✅ All inbound traffic inspected and filtered
- ✅ Only authorized traffic passes through
- ✅ Threats detected and blocked automatically
- ✅ Sensitive data protected with encryption
- ✅ Complete audit trail and compliance reporting
- ✅ Remote worker security with VPN
- ✅ Network segmentation with VLANs
- ✅ DDoS attack mitigation
For any business handling customer data, financial information, or intellectual property — a proper firewall is not optional. It is essential infrastructure.
Types of Firewalls We Offer
Stateful Firewalls
Understand the context of traffic. They do not just look at individual packets — they understand conversations. If an internal computer asks for data from the internet, the firewall allows that response. But unsolicited connections from the internet are blocked.
Examples: Cisco ASA, Fortinet FortiGate
Next-Generation Firewalls (NGFW)
Go beyond basic packet inspection. Understand applications running on your network. Can block specific applications while allowing others. Provide advanced threat protection and intrusion prevention.
Examples: Cisco ASA with threat subscriptions, Fortinet FortiGate
VPN Firewalls
Specialized for protecting remote workers and branch office connections. Handle large numbers of VPN tunnels while maintaining security.
Examples: Cisco ASA (250 tunnels), Fortinet FortiGate
Common Use Cases for Network Firewalls
ISP Infrastructure
ISPs use firewalls to:
- Protect their core network infrastructure
- Offer managed firewall services to subscribers
- Prevent attacks on their network
- Monitor and control customer traffic
Most ISPs in Bangladesh deploy enterprise firewalls like Cisco ASA or Fortinet FortiGate.
Corporate Networks
Corporate offices use firewalls to:
- Control employee internet access
- Prevent data exfiltration
- Protect company servers
- Enable secure remote worker access
- Enforce corporate security policies
A 100-person corporation typically deploys 1-2 firewalls at the network edge.
Data Centers
Data centers use firewalls to:
- Protect customer environments
- Segment networks for different clients
- Control traffic between servers
- Monitor for threats
- Meet compliance requirements
Data centers may have dozens of firewalls protecting different customer segments.
Hospitals and Medical Centers
Healthcare institutions use firewalls to:
- Protect patient privacy (HIPAA compliance)
- Prevent medical system breaches
- Secure patient data
- Comply with healthcare regulations
Medical data breaches can cost millions in fines and reputation damage.
Financial Institutions
Banks and financial companies use firewalls to:
- Comply with PCI-DSS (payment card) requirements
- Protect financial transactions
- Prevent fraud
- Secure customer banking data
Financial institutions use the most advanced firewall technology available.
Educational Institutions
Universities use firewalls to:
- Protect student and research data
- Control bandwidth usage
- Prevent academic resource theft
- Secure campus networks
Universities often manage large networks with multiple firewalls.
Government Offices
Government agencies use firewalls to:
- Protect classified information
- Secure communications
- Comply with security regulations
- Prevent cyber attacks
Government firewalls are the most heavily protected.
Firewall Features Explained
Stateful Inspection
The firewall remembers conversations. If your computer connects to a website, the firewall allows the website's response back. But random connections from the internet are rejected.
Access Control Lists (ACL)
Rules that define what traffic is allowed. You can block certain websites, restrict access by IP address, or allow specific applications only.
VPN Support
Allows secure encrypted connections for remote workers and branch offices. You can have 10, 100, or 250+ simultaneous VPN tunnels depending on firewall.
VLAN Support
Segment your network logically. Different departments or security levels can be isolated. Traffic between VLANs goes through the firewall for controlled access.
Intrusion Detection/Prevention (IDS/IPS)
Monitors network traffic for known attack signatures. Can automatically block detected threats.
DDoS Protection
Detects and mitigates Distributed Denial of Service attacks that try to overwhelm your network.
Content Filtering
Block access to malicious websites, inappropriate content, or company policy violations.
Application Awareness
Modern firewalls understand specific applications. Can block YouTube while allowing Google Workspace, for example.
Centralized Management
Manage multiple firewalls across different locations from a single dashboard.
High Availability / Redundancy
Two firewalls work together — if one fails, the other takes over automatically. Zero downtime.
Logging and Reporting
Complete audit trail of all network activity. Critical for compliance and forensic investigation.
Firewall Selection Guide
For Small Business (20-50 employees)
Recommended: Entry-level firewall (Cisco ASA 5515-X or equivalent)
Why:
- ✅ Adequate throughput for small office
- ✅ Support for VPN if remote workers needed
- ✅ Simple management
- ✅ Cost-effective
Typical features needed:
- 1 Gbps+ throughput
- 50-100 concurrent users
- Basic threat protection
- 1-2 WAN connections
For Growing Business (50-200 employees)
Recommended: Mid-range firewall (Cisco ASA 5525-X or equivalent)
Why:
- ✅ Better performance than entry-level
- ✅ Support for more VPN tunnels
- ✅ More advanced threat detection
- ✅ Room to grow
Typical features needed:
- 1-3 Gbps throughput
- 100-500 concurrent users
- Advanced threat protection
- Multiple WAN connections or redundancy
For Large Enterprise (200+ employees)
Recommended: High-performance firewall (Cisco ASA 5555-X or Fortinet FortiGate 3000 series)
Why:
- ✅ High throughput
- ✅ Support for large VPN deployments
- ✅ Advanced features like SSL inspection
- ✅ Scalable architecture
Typical features needed:
- 3+ Gbps throughput
- 500+ concurrent users
- Multiple 10 Gbps WAN links
- Multiple firewalls with load balancing
For ISP
Recommended: ISP-grade firewall (Cisco ASA 5525-X+, Fortinet FortiGate 3000+ series, or Juniper SRX)
Why:
- ✅ Can handle provider-class traffic volumes
- ✅ Support for many virtual circuits
- ✅ DDoS protection for subscribers
- ✅ Edge protection capabilities
ISPs need different requirements than enterprises. High throughput, many subscriber connections, carrier-grade reliability.
Firewall Brands Available
Cisco ASA Series
The industry standard. Used by ISPs, enterprises, and data centers worldwide. Proven reliability. Excellent support.
Popular models:
- ASA 5515-X — Entry level
- ASA 5525-X — Mid-range
- ASA 5555-X — High performance
Fortinet FortiGate Series
Advanced threat protection combined with competitive pricing. Growing rapidly in Bangladesh market.
Popular models:
- FortiGate 30E — Small office
- FortiGate 60D — Growing business
- FortiGate 3000 — Enterprise/ISP
Juniper SRX Series
Enterprise-grade firewalls with advanced routing and security features. Preferred by large ISPs and data centers.
Popular models:
- SRX110 — Branch office
- SRX340 — Mid-market
- SRX5800 — Large enterprise
Palo Alto Networks
Premium next-generation firewalls with advanced threat protection and application awareness.
Preferred by: Large enterprises, security-focused organizations
New vs Used/Refurbished Firewalls
Buy New If:
- ✅ Long-term investment (5+ years planned)
- ✅ Need latest threat intelligence
- ✅ Warranty is important
- ✅ Budget allows
New firewalls cost 40-60% more but include full warranty and manufacturer support.
Buy Refurbished If:
- ✅ Cost is primary concern
- ✅ Proven reliable model (older generation)
- ✅ Testing before larger deployment
- ✅ All critical security features needed (newer threats not a concern)
Refurbished firewalls are tested and work perfectly. Enterprise-grade hardware is built to last 7-10+ years.
Current Market Pricing in Bangladesh
| Firewall | New Price | Refurbished Price |
|---|---|---|
| Cisco ASA 5515-X | ৳800K-1M | ৳300K-500K |
| Cisco ASA 5525-X | ৳1.2M-1.5M | ৳500K-750K |
| Cisco ASA 5555-X | ৳2M-2.5M | ৳800K-1.2M |
| Fortinet FG 3000 | ৳1.5M-2M | ৳600K-900K |
| Juniper SRX340 | ৳1.8M-2.3M | ৳700K-1M |
Prices vary based on exact configuration, seller, and current market conditions.
Firewall Deployment Best Practices
1. Proper Planning
Before buying, understand:
- Current network usage patterns
- Expected growth over 3 years
- VPN requirements
- Compliance needs
- Budget constraints
2. Correct Sizing
Buy one model level above current needs. Do not buy exactly what you need today.
A firewall that is at 80% capacity already has no room for growth.
3. Redundancy
For mission-critical networks, deploy two firewalls in Active-Standby mode. If primary fails, secondary takes over automatically.
Redundancy costs 2x the firewall but provides 24/7 network availability.
4. Professional Configuration
Firewall configuration mistakes create security holes. Hire Cisco-certified professionals or experienced network engineers.
Misconfigured firewall is worse than no firewall.
5. Ongoing Management
- Update firmware regularly
- Monitor for threats and attacks
- Review logs regularly
- Test failover (if redundant)
- Plan capacity as network grows
6. Compliance and Auditing
Maintain audit logs for compliance purposes. Many regulations require:
- PCI-DSS (payment cards)
- HIPAA (healthcare)
- ISO 27001 (information security)
- SOC 2 (service organizations)
Firewall logs are your evidence of compliance.
Firewall Security Best Practices
Default Deny Policy
Configure firewall with "default deny" — block everything unless explicitly allowed. This is more secure than "default allow."
Principle of Least Privilege
Grant each user and device only the access they actually need. Not everything to everyone.
Regular Firmware Updates
Keep firmware current. Updates patch security vulnerabilities before attackers exploit them.
Strong Passwords and Access Control
Firewall admin password should be strong. Limit who can manage the firewall.
Backup Configuration
Back up firewall configuration regularly. If hardware fails, you can quickly restore settings to replacement unit.
Test Your Backup
Regularly test that backups work. A backup that cannot be restored is useless.
Monitor Firewall Health
Set up alerts for:
- High CPU or memory usage
- Failed backup attempts
- Unauthorized access attempts
- Hardware failures
When to Replace Your Firewall
Signs You Need to Upgrade:
❌ Firewall is consistently at 70%+ capacity
❌ New features needed (next-gen threat protection)
❌ Older model with no security updates available
❌ Hardware failing or parts no longer available
❌ Cannot meet compliance requirements
❌ Performance degrading over time
❌ End of life from manufacturer
Real-World Security Stories
Company Breached Through Old Firewall
A manufacturing company ran an old firewall model no longer receiving security updates. Hackers exploited a known vulnerability in the firewall itself. They gained access to the company's network, stole customer data, and compromised intellectual property.
Cost: ৳50 million in damages, lost customers, regulatory fines.
Lesson: Keep firewalls updated. Replace when no longer supported.
Ransomware Stopped by Firewall
A law firm was targeted by ransomware. The malware tried to download encryption tools and phone home to hacker command center.
The firewall blocked the command-and-control connection. The attack failed before reaching any servers.
Cost of firewall: ৳500K
Cost it prevented: ৳50M+ in ransom and downtime
Lesson: Good firewall pays for itself many times over.
VPN Protects Remote Worker
A company deployed AnyConnect VPN firewalls when remote work became necessary.
Employees connected from home through encrypted VPN tunnels. Their data was protected even on unsecured home WiFi.
When a competitor tried to steal trade secrets through an employee's home computer, they got only encrypted traffic — worthless to them.
Lesson: VPN firewalls enable secure remote work.
Browse Our Firewall Selection
We stock both new and refurbished enterprise firewalls from top manufacturers. Whether you need entry-level protection for a small office or carrier-grade firewalls for an ISP — we have the right solution.
Our firewall inventory includes:
- ✅ Cisco ASA series (5515-X through 5555-X)
- ✅ Fortinet FortiGate models
- ✅ Juniper SRX firewalls
- ✅ Palo Alto Networks (available upon request)
- ✅ Complete network security solutions
Each firewall is:
- ✅ Tested and verified working
- ✅ Properly configured and ready to deploy
- ✅ Transparent condition and specifications
- ✅ Local warranty and support
Get Expert Help
Choosing the right firewall is important. Wrong choice = inadequate security or wasted budget.
Our networking specialists can:
- ✅ Assess your current network
- ✅ Recommend appropriate firewall
- ✅ Help with sizing and capacity planning
- ✅ Assist with configuration
- ✅ Provide ongoing technical support
Contact us to discuss your network security requirements.